AI code review for GitHub, GitLab & Bitbucket
It reads the repo, not just the diff.
Before it says a word, the reviewer pulls in related files, the project structure and your conventions - so its comments read like they came from someone who knows the codebase.
Free for 14 days · No credit card · Installs in 60 seconds
#482 · billing
fix: retry failed charges
- Pull request openedcharge.ts · +8 −1
- Solemly reviewed the diffFollowed the change into errors.ts
- 1 P1 finding · merge blockedRetries can charge the card twice
- Ready to mergeAfter the fix is committed
Retries can charge the card twice. isRetryable treats a timeout as retryable (errors.ts:18), but a timed-out charge may have gone through. Send one idempotency key so a retry returns that charge instead of making a new one.
The kind of thing it catches
- P1Retry without an idempotency key
- P0SQL built from request input
- P1Token written to logs
- P2N+1 query inside a loop
- P1Admin route missing an auth check
- P2Race on a read-modify-write
- P0Secret committed to config
- P3Error swallowed by an empty catch
- P2Unbounded query on user input
- P1Webhook signature never verified
The life of a pull request
01 · Opens
A pull request opens.
From a coding agent, a copilot or someone on your team. The review starts the moment it does.
02 · Reads
It reads the repo, not just the diff.
Related files, the project's structure and your conventions, so comments read like they came from someone who knows the code.
03 · Reviews
Bugs and security, on every diff.
Separate passes look for what breaks and what leaks, and rank what they find by risk.
04 · Comments
Findings land on the lines that need them.
Inline comments on the diff and a summary at the top. Ask it why, right on the pull request.
05 · Gates
The merge waits until they're answered.
A merge status your branch protection can require. Fix the finding, or dismiss it with a reason.
06 · Merges
Then it merges.
Push a fix and the review updates in place, not a new wall of comments. Reviewed, answered, shipped.
The dashboard
Every review, finding and trend in one place.
The reviews land on the pull request. The dashboard is where you see all of them - across providers, repos and teams.
Every review, in one place
Reviews from GitHub, GitLab and Bitbucket in one list. Open any PR to read the summary, the inline comments and the security findings it got.
See where the risk is
Findings by severity, day by day, per repository — and how reviewed pull requests merge compared with unreviewed ones.
Reports you can hand to anyone
An executive summary with period-over-period changes, plus comparison, repo scorecard and author views. Export to CSV or print to PDF.
How AI-written code is landing
Solemly spots AI-authored pull requests from their commits and descriptions, then tracks how often they merge and how long they take.
It follows your house rules
CLAUDE.md, AGENTS.md and Cursor rules in each repo are read as conventions, so reviews hold code to your standards, not generic ones.




Watch it work
See a review catch a real bug.
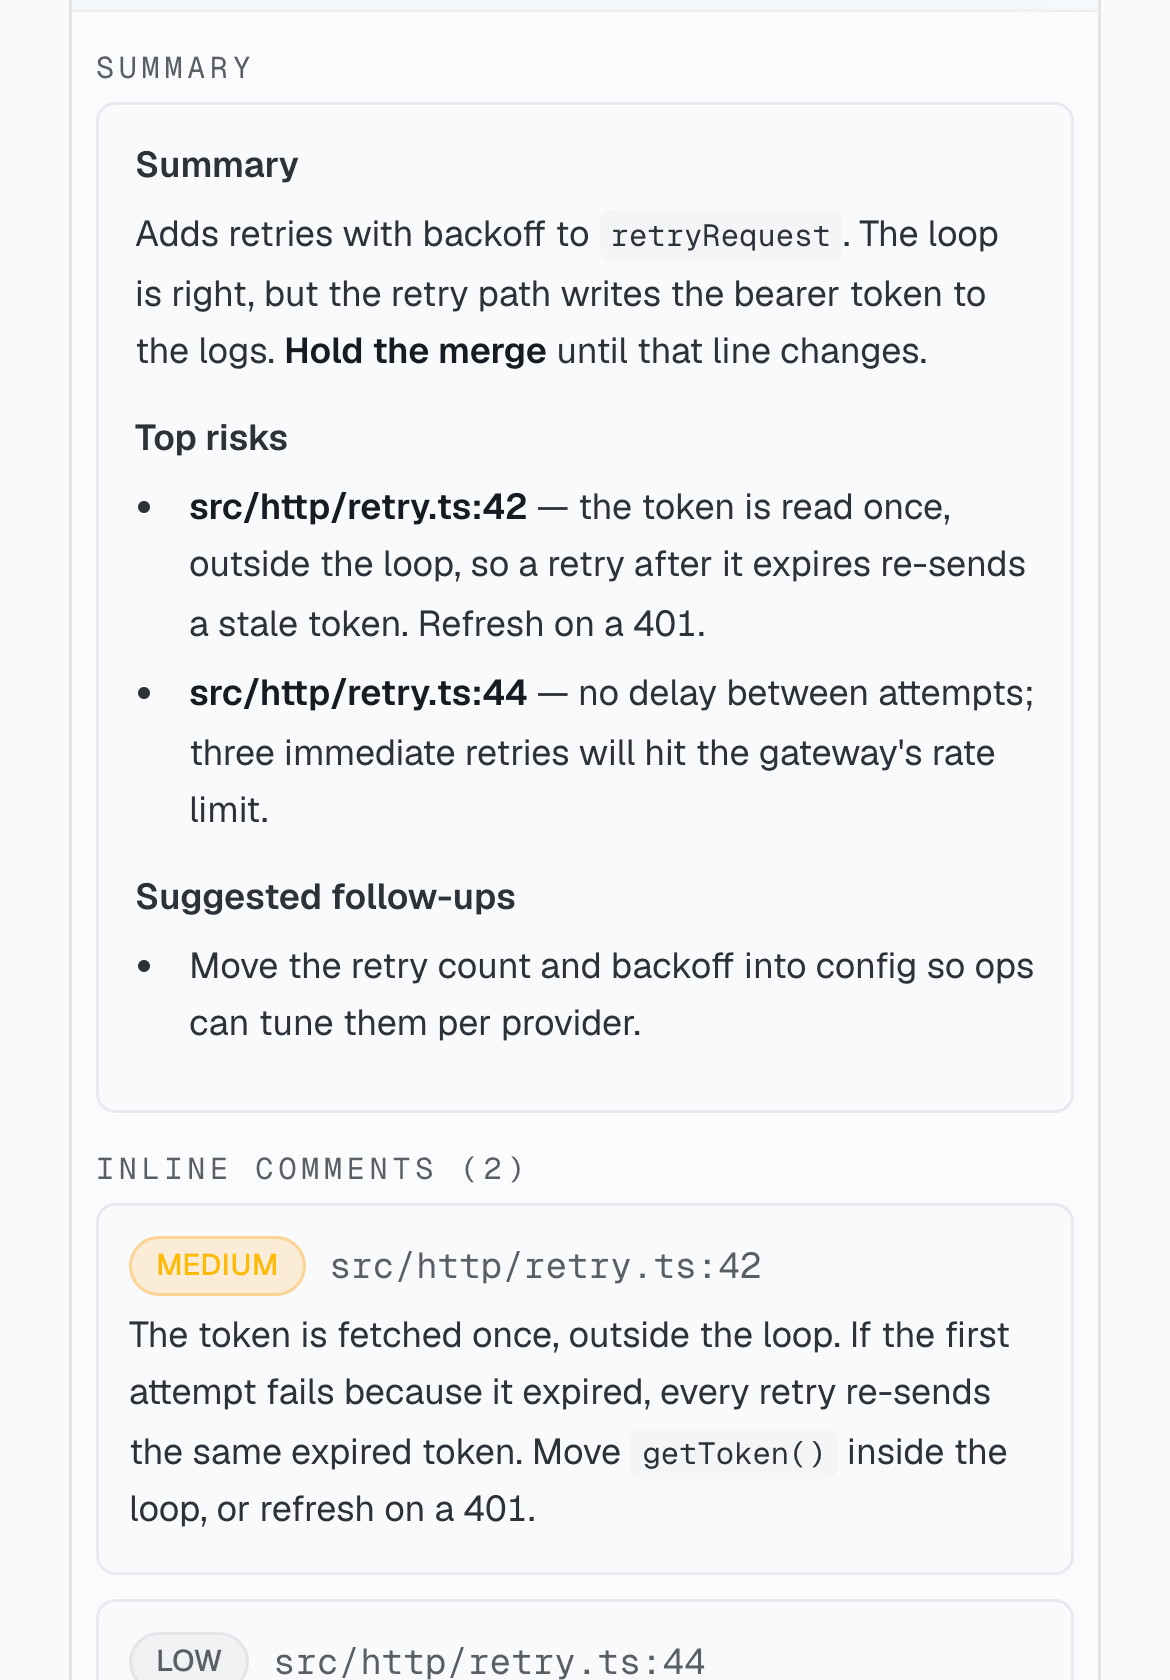
The demo is the whole product in under two minutes. The film is why it exists. The Shorts show a review catching a retry loop that writes the auth token to the logs, and a finding opened in your coding agent to fix.
Meet Solemly: AI code review with a merge gate, security scan and Jira acceptance checks
1:41A tour of the product: a review with inline findings, a security scan and a one-click hand-off to Claude Code, Cursor or Codex, then per-repo controls, Jira acceptance checks, analytics and the AI-impact reports.
How it reviews
A reviewer that knows the codebase and holds the line.
Before it says a word, the reviewer pulls in related files, the project structure and your conventions - so its comments read like they came from someone who knows the codebase.
- Follows CLAUDE.md, AGENTS.md and Cursor rules as house style
- Deep review mode searches and reads the repo before concluding
- A second pass re-checks every finding and drops the speculative ones
- Changedsrc/billing/charge.ts
- Importssrc/billing/errors.ts
- Importssrc/lib/stripe.ts
- Imported bysrc/checkout/submit.ts
- ConventionsCLAUDE.md
- Configpackage.json
- DocsREADME.md
- RequiredSolemly / ReviewBlocking: 1 high-severity finding
- Solemly / SecurityBlocking: 1 high-severity security finding
- Solemly / AcceptanceMatches the Jira ticket · PAY-412
The old session token is never revoked after a role change.
@solemly explain
issueToken() creates the new session, but nothing calls sessions.revoke() on the old one, and middleware/auth.ts accepts any unexpired token. A demoted admin keeps admin access for up to an hour.
- e41c0a9Review complete · 1 finding
- b7d2f13Superseded — a newer commit was pushed
- 9a0e6c2Superseded — a newer commit was pushed
Integrations
Works where your team already works.
One install per provider, no CI config or YAML. Open a pull request and the review lands natively on each platform.
GitHub
A GitHub App. Reviews land as native PR reviews with inline comments and required checks.
GitLab
Connect with an access token. Reviews post as MR notes with a commit status that gates the merge.
Bitbucket
Install the app on your workspace. Reviews post as PR comments with a build status for merge checks.
Jira
Finds the ticket from the branch, title or description and checks the PR against its acceptance criteria.
Slack
A message in the channel you pick the moment a review finishes: the PR, what was found, and a link.
Microsoft Teams
The same review notifications, posted to a Teams channel through an incoming webhook.
Set up in 60 seconds
Connect your repos
Install Solemly on your GitHub, GitLab or Bitbucket workspace and pick the repos to review.
Open a pull request
That's the trigger. The review starts straight away, with the surrounding repo in view.
The review lands on the PRdone
Ranked risks, inline comments on GitHub (a summary comment on GitLab and Bitbucket), a security pass, and a merge status you can require.
Also included
- PR descriptionsWritten for you, or on @solemly describe.
- Workspaces and teamsSeveral orgs, and teams that own their repos.
- Admin and member rolesAdmins run settings; members see their work.
- AI-authored PR detectionSpots AI-written PRs and tracks how they fare.
- Export and printReports to CSV, or a clean PDF.
- Sign in your wayEmail, or GitHub, GitLab or Bitbucket.
Independent benchmark
Within a point of Greptile on Martian's Code Review Bench.
50 real pull requests from Sentry, Cal.com, Grafana, Keycloak and Discourse, scored by an LLM judge against human-checked bugs. One trial, run by us on 21 October 2026: 10th of 22 tools, with the leaders near 59.
- Greptile45.0
- Solemly44.0
- GitHub Copilot43.6
- Claude Code40.6
- CodeRabbit38.6
Pricing
Simple, honest pricing.
Free 14-day trial, then pay per user. 40 PR reviews per user every month. Cancel anytime.